On this page
- Summary
- Overview
- Cloud TTPs
- Initial Access · T1078.004 — Valid Accounts: Cloud Accounts
- Execution · T1059.009 — Command and Scripting Interpreter: Cloud API
- Persistence · T1543.005 — Create or Modify System Process: Container Services
- Defense Evasion · T1578 — Modify Cloud Compute Infrastructure
- Collection · T1530 — Data from Cloud Storage
- Command and Control · T1071 — Application Layer Protocol
- Exfiltration · T1041 — Exfiltration Over C2 Channel
- Inferences and Limitations
- Incident Response Steps
- 1. Investigate Suspicious CLI API Activity
- 2. Investigate Unauthorized SSH Security Group Changes
- 3. Contain Cloud Data Store Access
- 4. Trace SSH C2 Paths in Network Logs
- 5. Remediate Compromised IAM Keys
- Getting Help
- About Invictus Incident Response
Summary
- Threat Actor: Sea Turtle (Türkiye-nexus), a.k.a. Teal Kurma, Cosmic Wolf, Marbled Dust
- Motivation: State-affiliated espionage
- Targeting: AWS and/or Azure environments, Government, Internet Service Providers, Technology, Telecommunications, etc.
- Attack Types: DNS-hijacking, zero-day exploitation, credentials and cloud storage theft, etc.
- Defenses: Identity security, storage protection, network traffic monitoring, vulnerability management, etc.
If you enjoy reading about cloud threat actors, you might also enjoy our training or investigating your own cloud incidents with Cloud Labs.
Overview
Sea Turtle is a Türkiye-nexus threat actor known for conducting state-affiliated espionage operations since at least 2017. The group has primarily targeted government agencies, IT service providers, and the telecommunications sector, with a notable evolution in tactics over the past decade.
Sea Turtle initially gained attention for its DNS hijacking campaigns, which redirected traffic to steal credentials, often targeting Middle Eastern and European entities. This activity persisted from 2017 through 2020. By 2021, the group had shifted toward exploiting exposed credentials and known vulnerabilities to gain access to internet service providers and related infrastructure, often as a path to reach downstream victims. This mentioned activity continued into 2023, when Sea Turtle was observed deploying a custom Linux/Unix implant and expanding into cloud-focused intrusions.
In one case, the group targeted a technology company’s cloud environment using stolen credentials to attempt data theft. Using the cloud environments command line they altered security group settings to allow direct Secure Shell (SSH) access. Since April 2024, Sea Turtle has been observed exploiting unpatched user accounts vulnerable to a zero-day (CVE-2025-27920) in Output Messenger, a cross-platform enterprise messaging application.
Cloud TTPs
All of the details below are also available in our GitHub repository, which provides background on each observed technique along with corresponding MITRE ATT&CK mappings, making it easy to map these insights directly to your cloud logs.
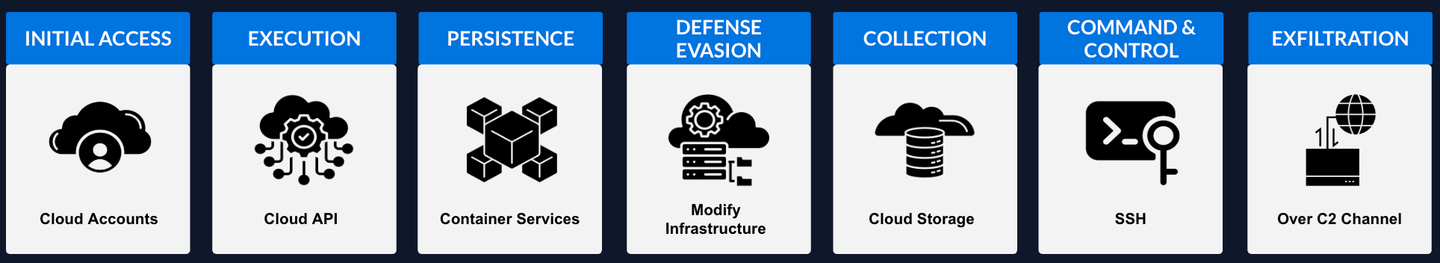
Initial Access · T1078.004 — Valid Accounts: Cloud Accounts
Sea Turtle used stolen AWS IAM keys or Azure Entra ID credentials to authenticate and access cloud environments, enabling unauthorized API calls.
Execution · T1059.009 — Command and Scripting Interpreter: Cloud API
Executed malicious commands via AWS CLI or Azure CLI/PowerShell to manage resources (EC2/S3/IAM; VMs/Blob/Entra ID).
Persistence · T1543.005 — Create or Modify System Process: Container Services
Modified security group rules to allow SSH (22) from attacker infrastructure, ensuring persistent access.
Defense Evasion · T1578 — Modify Cloud Compute Infrastructure
Opened SSH by altering network controls, blending with legit admin activity to evade detection.
Collection · T1530 — Data from Cloud Storage
Queried or downloaded sensitive data from cloud storage/compute using stolen credentials and CLI access.
Command and Control · T1071 — Application Layer Protocol
Used SSH (TCP/22) as the C2 channel to manage compromised instances remotely.
Exfiltration · T1041 — Exfiltration Over C2 Channel
Likely transferred data to actor infrastructure through the established SSH-based C2 channel.
Inferences and Limitations
In CrowdStrike’s 2023 Cloud Risk Report, they briefly describe how Cosmic Wolf (a.k.a. Sea Turtle), targeted data in a victim’s cloud environment. The report is provider-agnostic, yet the combination of ‘security group’ changes and CLI usage suggests either AWS or Azure.
Additionally, we assess it is likely the actor used T1530 (Data from Cloud Storage Object) and T1537 (Exfiltration to Cloud Account), inferred from the objective of targeting stored cloud data; this is consistent with common cloud-intrusion tradecraft. However, the report does not provide details on:
- How credentials were stolen;
- What specific data was accessed (e.g., S3 vs. RDS); or
- Whether any exfiltration was confirmed.
Furthermore, there is no mention of the use of other services (e.g., Lambda, IAM role creation, or temporary credentials), which limits visibility into potential persistence or privilege escalation techniques (e.g., T1078.004, T1098).
Incident Response Steps
Below are several high-impact steps to prepare for and respond to the TTPs mentioned above. The list isn’t exhaustive, but it highlights key areas where defenders can focus their efforts. Click each step to view additional details.
1. Investigate Suspicious CLI API Activity
Confirm scope of compromise from unauthorized CLI usage.
Scroll horizontally on narrow screens.
Action | AWS | Azure |
|---|---|---|
Investigate |
|
|
Harden |
|
|
2. Investigate Unauthorized SSH Security Group Changes
Confirm persistent access via modified security group rules.
Scroll horizontally on narrow screens.
Action | AWS | Azure |
|---|---|---|
Investigate |
|
|
Harden |
|
|
3. Contain Cloud Data Store Access
Block unauthorized access to sensitive data stores.
Scroll horizontally on narrow screens.
Action | AWS | Azure |
|---|---|---|
Investigate |
|
|
Harden |
|
|
4. Trace SSH C2 Paths in Network Logs
Identify threat actor’s command-and-control (C2) connections.
Scroll horizontally on narrow screens.
Action | AWS | Azure |
|---|---|---|
Investigate |
|
|
Harden |
|
|
5. Remediate Compromised IAM Keys
Neutralize stolen credentials to halt threat actor access.
Scroll horizontally on narrow screens.
Action | AWS | Azure |
|---|---|---|
Investigate |
|
|
Harden |
|
|
Getting Help
If you spot any of these TTPs or indicators in your environment, or just want to become incident-ready in the cloud, contact our team. We’ll help you tighten your AWS defenses, refine your IR runbook, and stay ahead of Sea Turtle or other cloud-focused adversaries.
About Invictus Incident Response
We are an incident response company and we ❤️ the cloud and specialize in supporting organizations in preparing and responding to a cyber attack. We help our clients stay undefeated!
🆘 Incident Response support reach out to cert@invictus-ir.com or go to https://www.invictus-ir.com/24-7